Minimize Cybersecurity Risk with the Known Exploited Vulnerabilities (KEV) Catalog
In November 2021 the Cybersecurity and Infrastructure Security Agency (CISA) started the Known Exploited Vulnerabilities (KEV) Catalog and Binding Operational Directive 22-01. The KEV catalog lists only vulnerabilities known to be actively exploited.
KEV Catalog: “PrintNightmare” (CVE-2021-34527)
CVE-2021-34527 is a critical Windows Print Spooler vulnerability that allowed malicious actors to remotely inject DLLs and get administrative rights.
KEV Catalog: “ZeroLogon” NetLogon Privilege Escalation Vulnerability (CVE-2020-1472)
In July 2020 a critical privilege escalation vulnerability emerged that affected Active Directory environments: CVE-2020-1472. Nicknamed “ZeroLogon”, the vulnerability was
Active Directory Series: Introducing AD CS
This post introduces Active Directory Certificate Services (AD CS) and topics like: public key infrastructure (PKI), the Kerberos pre-authentication protocol PKINIT, Certificate Signing Requests (CSR), and templates. This overview provides a baseline for learning AD CS penetration testing.
KEV Catalog: “SMBGhost” Microsoft SMBv3 Remote Code Execution Vulnerability (CVE-2020-0796)
“SMBGhost” is a critical vulnerability that affected SMBv3 in Windows 10 Versions 1903 and 1909. The vulnerability is an integer
KEV Catalog: “HiveNightmare” aka ”SeriousSAM” Vulnerability CVE-2021-36934
CVE-201-36934 is called Microsoft Windows SAM Local Privilege Escalation Vulnerability and is also known by the nicknames “HiveNightmare” or “SeriousSAM”.
SEIZING THE SKIES: THE STRATEGIC ADVANTAGE OF AI IN A POST-BAN WORLD
Folllowing the ban of DJI drones in Florida, Secured offers a unique drone surveillance solution with its AI Object Recognition
Empowering American Heroes: The Significance of the Service-Disabled Veteran-Owned Small Business Program
We, here at Secured™, are proud to announce that we have officially achieved the highly regarded designation of “Service-Disabled Veteran-Owned

The Rise of AI-Powered Cyber Attacks: Are We Prepared?
Cybercriminals are leveraging AI’s capabilities to execute more sophisticated and evasive attacks, putting sensitive data and critical infrastructure at more
Lessons From the City Of Dallas Ransomware Attack
Two weeks ago, the City of Dallas was targeted by the suspected ransomware group Royal. There are specific best practices

Secured™ Takes Aim To Support Veterans As “Top Gun” Sponsor of BCV’s Annual Helicopter Hog Hunt Weekend
We were proud to sponsor this year’s Big Country Veterans’ (BCV) Helicopter Hog Hunt Weekend, as well as honor a
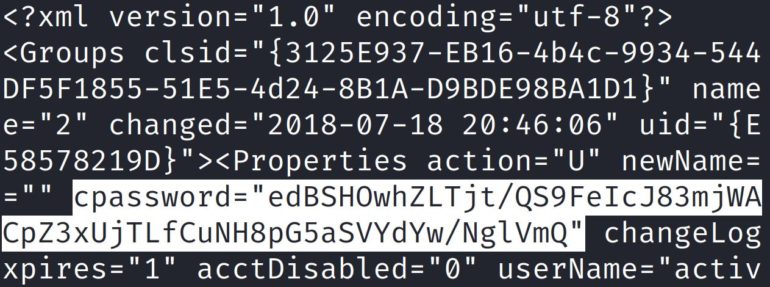
7 Locations for Unsecured Credentials
Attackers can use unsecured user credentials to access different services and pivot within a network. Malicious actors and penetration testers