Minimize Cybersecurity Risk with the Known Exploited Vulnerabilities (KEV) Catalog
In November 2021 the Cybersecurity and Infrastructure Security Agency (CISA) started the Known Exploited Vulnerabilities (KEV) Catalog and Binding Operational Directive 22-01. The KEV catalog lists only vulnerabilities known to be actively exploited.
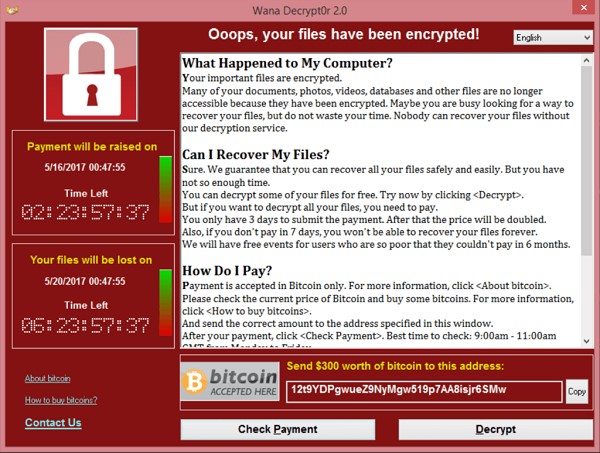
KEV Catalog: “WannaCry” Microsoft SMBv1 RCE Vulnerability (CVE-2017-0143)
CVE-2017-0143 is a notorious Microsoft Windows SMBv1 remote code execution vulnerability. This vulnerability and the EternalBlue exploit led to the
KEV Catalog: 3 Linux Privilege Escalation Vulnerabilities
Legacy Linux environments are open to various privilege escalation vulnerabilities. This post reviews three well-known vulnerabilities.
Active Directory Series: Introducing AD CS
This post introduces Active Directory Certificate Services (AD CS) and topics like: public key infrastructure (PKI), the Kerberos pre-authentication protocol PKINIT, Certificate Signing Requests (CSR), and templates. This overview provides a baseline for learning AD CS penetration testing.
KEV Catalog: “ZeroLogon” NetLogon Privilege Escalation Vulnerability (CVE-2020-1472)
In July 2020 a critical privilege escalation vulnerability emerged that affected Active Directory environments: CVE-2020-1472. Nicknamed “ZeroLogon”, the vulnerability was
Active Directory Series: Silver Ticket Attack
Silver Ticket attacks are a well-known credential access attack in Active Directory environments that focuses on forging Kerberos Service Tickets
Reports: Rapid Rise In Open Source Supply Chain Attacks
Last month, Mend released their Open Source Risk Report which outlines the risks associated with open source vulnerabilities and software
Converge Cybersecurity and Physical Security to Protect the U.S. Electrical Grid
On February 6th law enforcement officials charged a neo-Nazi leader and his associate with plotting to attack Baltimore’s power grid.

6 Cloud Security Issues and AWS solutions in 2023
In 2023, many companies seeking to reduce IT costs are also turning to the cloud. Cloud adoption provides numerous benefits

Cybersecurity Teams: An Introduction to Blue Team
Blue Team provides a variety of defensives services: network vulnerability evaluations, mitigation recommendations, real time threat detection, and overall readiness

Secured™ Awarded Over $4,000,000 for Humanitarian Support
Secured™ has been awarded over $4,000,000 in Unmanned Aerial Systems (UAS) customization and development in 2023 to assist in global
Defending Against Cyber Threats in the Oil and Gas Sector
The last decade has seen a global rise in cybersecurity attacks on the oil and gas sector.