Minimize Cybersecurity Risk with the Known Exploited Vulnerabilities (KEV) Catalog
In November 2021 the Cybersecurity and Infrastructure Security Agency (CISA) started the Known Exploited Vulnerabilities (KEV) Catalog and Binding Operational Directive 22-01. The KEV catalog lists only vulnerabilities known to be actively exploited.
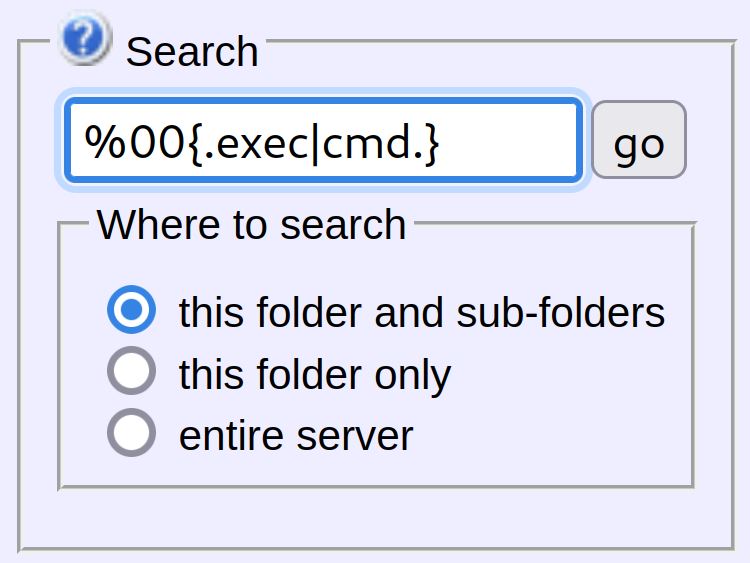
KEV Catalog: Rejetto HTTP File Server Remote Code Execution Vulnerability (CVE-2014-6287)
CVE-2014-6287 is a remote code execution vulnerability in Rejetto HTTP File Server versions before 2.3c. Attackers could execute arbitrary code
KEV Catalog: “Heartbleed” OpenSSL Vulnerability (CVE-2014-0160)
CVE-2014-0160 is known by the nickname “Heartbleed”. It is an information disclosure vulnerability in outdated versions of OpenSSL, specifically the
Active Directory Series: Introducing AD CS
This post introduces Active Directory Certificate Services (AD CS) and topics like: public key infrastructure (PKI), the Kerberos pre-authentication protocol PKINIT, Certificate Signing Requests (CSR), and templates. This overview provides a baseline for learning AD CS penetration testing.
KEV Catalog: “PrintNightmare” (CVE-2021-34527)
CVE-2021-34527 is a critical Windows Print Spooler vulnerability that allowed malicious actors to remotely inject DLLs and get administrative rights.
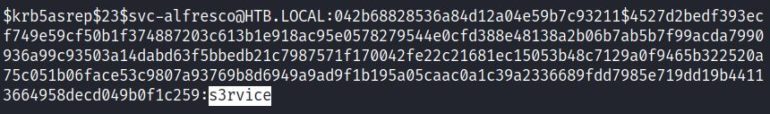
Active Directory Series: AS-REP Roasting
AS-REP roasting focuses on cracking the passwords of Active Directory accounts that do not have Kerberos preauthentication set.
Dallas County Data Incident from Computers Sold at Auction
Last month, Dallas County released a notice disclosing that Dallas County computers were sold at auction that did not have

Ferrari Cyber Incident: Cyber Extortion vs Ransomware
Last week, Ferrari announced it was contacted by a cyber threat actor for a ransom demand. Their corporate response to
CISA Announces Ransomware Vulnerability Warning Pilot
Last week, Monday March 13, CISA announced the creation of the Ransomware Vulnerability Warning Pilot (RVWP). This program was launched
Introducing and Setting Up the New Kali Linux 2023.1: Kali Purple
Today, Kali Linux’s 10-year anniversary, Kali Linux released their newest Kali Linux version: Kali Purple. Kali Linux is known for

An Overview of the Biden-Harris New National Cyber Security Strategy
The key messages emphasize where the U.S. government wants to allocate its cybersecurity spending and who should be responsible for

DDoS Attacks Emerge as Main Cyber Threat in Ukraine Conflict
The CyberPeace Institute has recorded cyber-attacks against a variety of host nations, including Ukraine and Russia. Reviewing their data from